diff --git a/README.md b/README.md
index 5cb8afde56..2c58e1746e 100644
--- a/README.md
+++ b/README.md
@@ -216,7 +216,7 @@ Prowler has two parameters related to regions: `-r` that is used query AWS servi
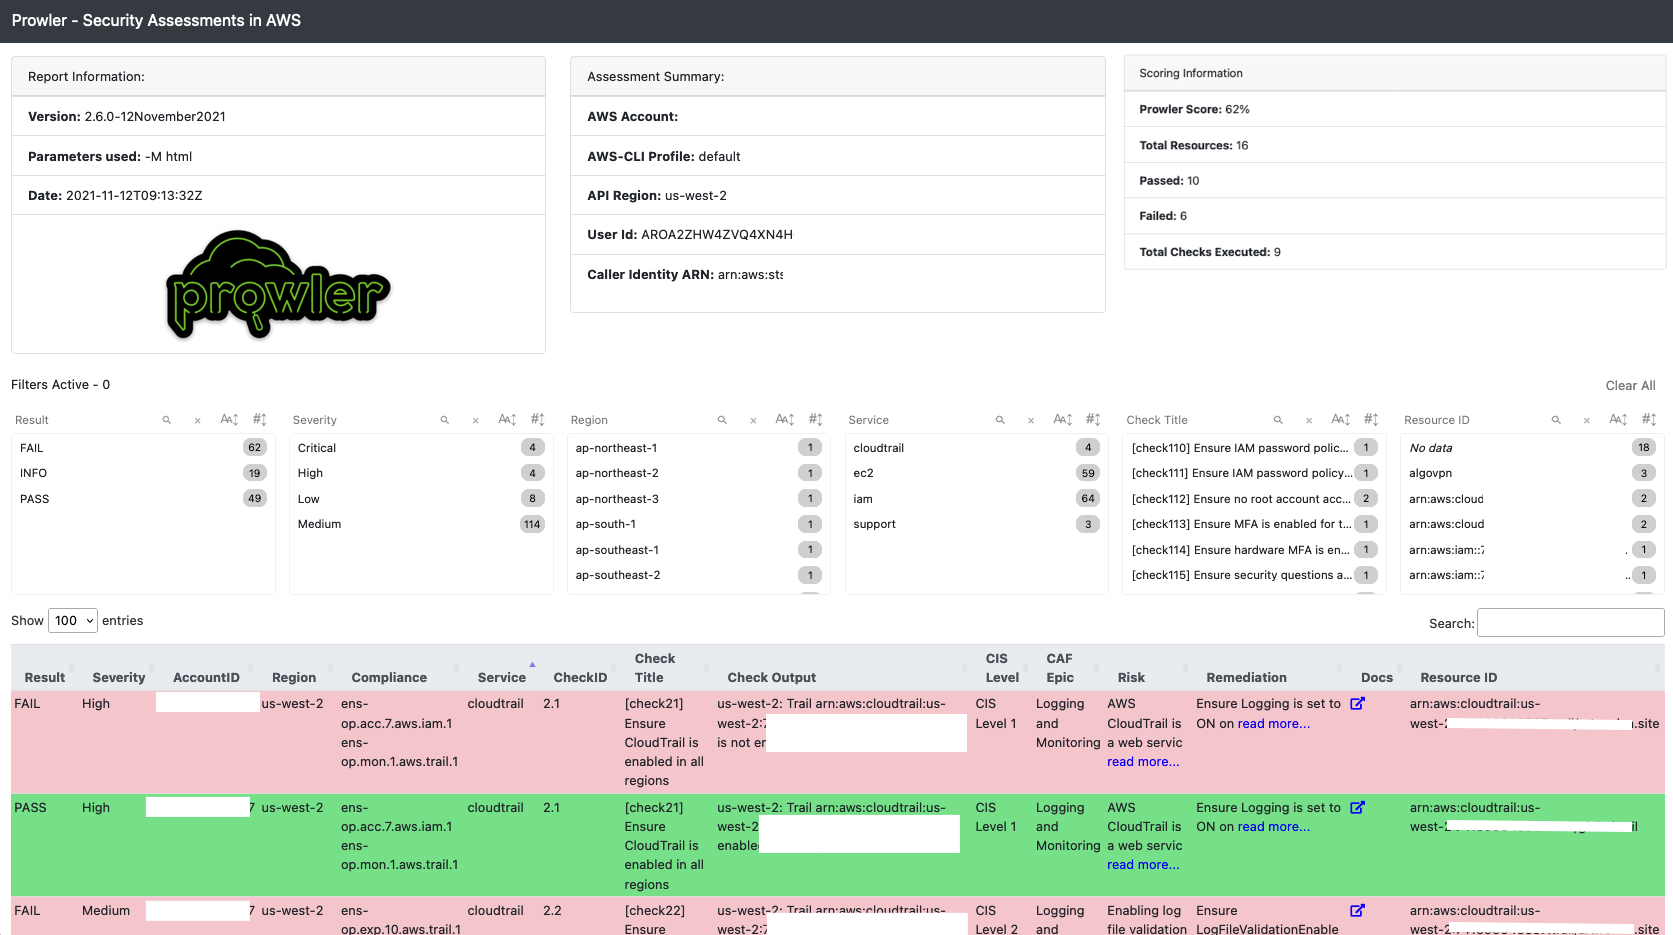 -- Sample screenshot of the Quicksight dashboard, see [https://quicksight-security-dashboard.workshop.aws](quicksight-security-dashboard.workshop.aws/):
+- Sample screenshot of the Quicksight dashboard, see [https://quicksight-security-dashboard.workshop.aws](https://quicksight-security-dashboard.workshop.aws/):
 diff --git a/checks/check_extra7160 b/checks/check_extra7160
new file mode 100644
index 0000000000..8016819ee8
--- /dev/null
+++ b/checks/check_extra7160
@@ -0,0 +1,42 @@
+#!/usr/bin/env bash
+
+# Prowler - the handy cloud security tool (copyright 2021) by Toni de la Fuente
+#
+# Licensed under the Apache License, Version 2.0 (the "License"); you may not
+# use this file except in compliance with the License. You may obtain a copy
+# of the License at http://www.apache.org/licenses/LICENSE-2.0
+#
+# Unless required by applicable law or agreed to in writing, software distributed
+# under the License is distributed on an "AS IS" BASIS, WITHOUT WARRANTIES OR
+# CONDITIONS OF ANY KIND, either express or implied. See the License for the
+# specific language governing permissions and limitations under the License.
+CHECK_ID_extra7160="7.160"
+CHECK_TITLE_extra7160="[extra7160] Check if Redshift has automatic upgrades enabled"
+CHECK_SCORED_extra7160="NOT_SCORED"
+CHECK_CIS_LEVEL_extra7160="EXTRA"
+CHECK_SEVERITY_extra7160="Medium"
+CHECK_ASFF_RESOURCE_TYPE_extra7160="AwsRedshift"
+CHECK_ALTERNATE_check7160="extra7160"
+CHECK_SERVICENAME_extra7160="redshift"
+CHECK_RISK_extra7160='Without automatic version upgrade enabled; a critical Redshift Cluster version can become severly out of date.'
+CHECK_REMEDIATION_extra7160='Enabled AutomaticVersionUpgrade on Redshift Cluster'
+CHECK_DOC_extra7160='https://docs.aws.amazon.com/redshift/latest/mgmt/managing-cluster-operations.html'
+CHECK_CAF_EPIC_extra7160='Infrastructure Security'
+
+extra7160(){
+ for regx in $REGIONS; do
+ LIST_OF_CLUSTERS=$($AWSCLI redshift describe-clusters $PROFILE_OPT --query 'Clusters[*].ClusterIdentifier' --region $regx --output text)
+ if [[ $LIST_OF_CLUSTERS ]]; then
+ for cluster in $LIST_OF_CLUSTERS; do
+ AUTO_UPGRADE_ENABLED=$($AWSCLI redshift describe-clusters $PROFILE_OPT --cluster-identifier $cluster --query 'Clusters[*].AllowVersionUpgrade' --region $regx --output text)
+ if [[ $AUTO_UPGRADE_ENABLED == "True" ]]; then
+ textPass "$regx: $cluster has AllowVersionUpgrade enabled" "$regx" "$cluster"
+ else
+ textFail "$regx: $cluster has AllowVersionUpgrade disabled" "$regx" "$cluster"
+ fi
+ done
+ else
+ textInfo "$regx: No Redshift Clusters found" "$regx"
+ fi
+ done
+}
\ No newline at end of file
diff --git a/checks/check_extra7161 b/checks/check_extra7161
new file mode 100644
index 0000000000..1de051c370
--- /dev/null
+++ b/checks/check_extra7161
@@ -0,0 +1,43 @@
+#!/usr/bin/env bash
+
+# Prowler - the handy cloud security tool (copyright 2018) by Toni de la Fuente
+#
+# Licensed under the Apache License, Version 2.0 (the "License"); you may not
+# use this file except in compliance with the License. You may obtain a copy
+# of the License at http://www.apache.org/licenses/LICENSE-2.0
+#
+# Unless required by applicable law or agreed to in writing, software distributed
+# under the License is distributed on an "AS IS" BASIS, WITHOUT WARRANTIES OR
+# CONDITIONS OF ANY KIND, either express or implied. See the License for the
+# specific language governing permissions and limitations under the License.
+CHECK_ID_extra7161="7.161"
+CHECK_TITLE_extra7161="[extra7161] Check if EFS have protects sensative data with encryption at rest"
+CHECK_SCORED_extra7161="NOT_SCORED"
+CHECK_CIS_LEVEL_extra7161="EXTRA"
+CHECK_SEVERITY_extra7161="Medium"
+CHECK_ASFF_RESOURCE_TYPE_extra7161="AwsEfsFileSystem"
+CHECK_ALTERNATE_check7161="extra7161"
+CHECK_SERVICENAME_extra7161="efs"
+CHECK_RISK_extra7161='EFS should be encrypted at rest to prevent exposure of sensitive data to bad actors'
+CHECK_REMEDIATION_extra7161='Ensure that encryption at rest is enabled for EFS file systems. Encryption at rest can only be enabled during the file system creation.'
+CHECK_DOC_extra7161='https://docs.aws.amazon.com/efs/latest/ug/encryption-at-rest.html'
+CHECK_CAF_EPIC_extra7161='Data Protection'
+
+extra7161(){
+ # "Check if EFS has encryption at rest enabled (Not Scored) (Proposed requirement for 1.5 CIS benchmark)"
+ for regx in $REGIONS; do
+ LIST_OF_EFS_IDS=$($AWSCLI efs describe-file-systems $PROFILE_OPT --region $regx --query 'FileSystems[*].FileSystemId' --output text | xargs -n1)
+ if [[ $LIST_OF_EFS_IDS ]]; then
+ for efsId in $LIST_OF_EFS_IDS;do
+ EFS_ENCRYPTION_CHECK=$($AWSCLI efs $PROFILE_OPT describe-file-systems --region $regx --file-system-id $efsId --output json --query 'FileSystems[*].Encrypted' --output text)
+ if [[ $EFS_ENCRYPTION_CHECK == "True" ]]; then
+ textPass "$regx: EFS $efsId has has encryption at rest enabled" "$regx" "$efsId"
+ else
+ textFail "$regx: EFS: $efsId does not have encryption at rest enabled" "$regx" "$efsId"
+ fi
+ done
+ else
+ textInfo "$regx: No EFS found" "$regx"
+ fi
+ done
+}
diff --git a/checks/check_extra7162 b/checks/check_extra7162
new file mode 100644
index 0000000000..f0f51199f0
--- /dev/null
+++ b/checks/check_extra7162
@@ -0,0 +1,50 @@
+#!/usr/bin/env bash
+
+# Prowler - the handy cloud security tool (copyright 2018) by Toni de la Fuente
+#
+# Licensed under the Apache License, Version 2.0 (the "License"); you may not
+# use this file except in compliance with the License. You may obtain a copy
+# of the License at http://www.apache.org/licenses/LICENSE-2.0
+#
+# Unless required by applicable law or agreed to in writing, software distributed
+# under the License is distributed on an "AS IS" BASIS, WITHOUT WARRANTIES OR
+# CONDITIONS OF ANY KIND, either express or implied. See the License for the
+# specific language governing permissions and limitations under the License.
+CHECK_ID_extra7162="7.162"
+CHECK_TITLE_extra7162="[extra7162] Check if CloudWatch Log Groups have a retention policy of 365 days"
+CHECK_SCORED_extra7162="NOT_SCORED"
+CHECK_CIS_LEVEL_extra7162="EXTRA"
+CHECK_SEVERITY_extra7162="Medium"
+CHECK_ASFF_RESOURCE_TYPE_extra7162="AwsLogsLogGroup"
+CHECK_ALTERNATE_check7162="extra7162"
+CHECK_SERVICENAME_extra7162="cloudwatch"
+CHECK_RISK_extra7162='If log groups have a low retention policy of less than 365 days, crucial logs and data can be lost'
+CHECK_REMEDIATION_extra7162='Add Log Retention policy of 365 days to log groups. This will persist logs and traces for a long time.'
+CHECK_DOC_extra7162='https://docs.aws.amazon.com/AWSCloudFormation/latest/UserGuide/AWS_Logs.html'
+CHECK_CAF_EPIC_extra7162='Data Retention'
+
+extra7162() {
+ # "Check if CloudWatch Log Groups have a retention policy of 365 days"
+ declare -i LOG_GROUP_RETENTION_PERIOD_DAYS=365
+ for regx in $REGIONS; do
+ LIST_OF_365_RETENTION_LOG_GROUPS=$($AWSCLI logs describe-log-groups $PROFILE_OPT --region $regx --query 'logGroups[?retentionInDays=="${LOG_GROUP_RETENTION_PERIOD_DAYS}"].[logGroupName]' --output text)
+ if [[ $LIST_OF_365_RETENTION_LOG_GROUPS ]]; then
+ for log in $LIST_OF_365_RETENTION_LOG_GROUPS; do
+ textPass "$regx: $log Log Group has 365 days retention period!" "$regx" "$log"
+ done
+ fi
+ LIST_OF_NON_365_RETENTION_LOG_GROUPS=$($AWSCLI logs describe-log-groups $PROFILE_OPT --region $regx --query 'logGroups[?retentionInDays!="${LOG_GROUP_RETENTION_PERIOD_DAYS}"].[logGroupName]' --output text)
+ if [[ $LIST_OF_NON_365_RETENTION_LOG_GROUPS ]]; then
+ for log in $LIST_OF_NON_365_RETENTION_LOG_GROUPS; do
+ textFail "$regx: $log Log Group does not have 365 days retention period!" "$regx" "$log"
+ done
+ fi
+ REGION_NO_LOG_GROUP=$($AWSCLI logs describe-log-groups $PROFILE_OPT --region $regx --output text)
+ if [[ $REGION_NO_LOG_GROUP ]]; then
+ :
+ else
+ textInfo "$regx does not have a Log Group!" "$regx"
+
+ fi
+ done
+}
diff --git a/checks/check_extra7163 b/checks/check_extra7163
new file mode 100644
index 0000000000..60bf8750a0
--- /dev/null
+++ b/checks/check_extra7163
@@ -0,0 +1,57 @@
+#!/usr/bin/env bash
+
+# Prowler - the handy cloud security tool (copyright 2019) by Toni de la Fuente
+#
+# Licensed under the Apache License, Version 2.0 (the "License"); you may not
+# use this file except in compliance with the License. You may obtain a copy
+# of the License at http://www.apache.org/licenses/LICENSE-2.0
+#
+# Unless required by applicable law or agreed to in writing, software distributed
+# under the License is distributed on an "AS IS" BASIS, WITHOUT WARRANTIES OR
+# CONDITIONS OF ANY KIND, either express or implied. See the License for the
+# specific language governing permissions and limitations under the License.
+
+# Remediation:
+#
+# https://docs.aws.amazon.com/cli/latest/reference/secretsmanager/rotate-secret.html
+#
+# rotate-secret
+# --secret-id
+# [--client-request-token ]
+# [--rotation-lambda-arn ]
+# [--rotation-rules ]
+# [--cli-input-json ]
+# [--generate-cli-skeleton ]
+
+
+CHECK_ID_extra7163="7.163"
+CHECK_TITLE_extra7163="[extra7163] Check if Secrets Manager key rotation is enabled"
+CHECK_SCORED_extra7163="NOT_SCORED"
+CHECK_TYPE_extra7163="EXTRA"
+CHECK_SEVERITY_extra7163="Medium"
+CHECK_ASFF_RESOURCE_TYPE_extra7163="AwsSecretsManagerSecret"
+CHECK_ALTERNATE_extra7163="extra7163"
+CHECK_SERVICENAME_extra7163="secretsmanager"
+CHECK_RISK_extra7163="Rotating secrets minimizes exposure to attacks using stolen keys."
+CHECK_REMEDITATION_extra7163="Enable key rotation on Secrets Manager key."
+CHECK_DOC_extra7163="https://docs.aws.amazon.com/secretsmanager/latest/userguide/rotating-secrets_strategies.html"
+CHECK_CAF_EPIC_extra7163="Data Protection"
+
+extra7163(){
+ # "Check if Secrets Manager key rotation is enabled"
+ for regx in $REGIONS; do
+ LIST_OF_SECRETS=$($AWSCLI secretsmanager list-secrets $PROFILE_OPT --region $regx --query 'SecretList[*].Name' --output text)
+ if [[ $LIST_OF_SECRETS ]]; then
+ for secret in $LIST_OF_SECRETS; do
+ KEY_ROTATION_ENABLED=$($AWSCLI secretsmanager describe-secret $PROFILE_OPT --region $regx --secret-id $secret --output json | jq '.RotationEnabled')
+ if [[ $KEY_ROTATION_ENABLED == true ]]; then
+ textPass "$regx: $secret has key rotation enabled." "$regx" "$secret"
+ else
+ textFail "$regx: $secret does not have key rotation enabled." "$regx" "$secret"
+ fi
+ done
+ else
+ textPass "$regx: No Secrets Manager secrets found." "$regx"
+ fi
+ done
+}
diff --git a/include/assume_role b/include/assume_role
index d15d70b5e5..0d5e592842 100644
--- a/include/assume_role
+++ b/include/assume_role
@@ -11,9 +11,9 @@
# CONDITIONS OF ANY KIND, either express or implied. See the License for the
# specific language governing permissions and limitations under the License.
-# both variables are mandatory to be set together
assume_role(){
- if [[ -z $ROLE_TO_ASSUME ]]; then
+ # Both variables are mandatory to be set togethe
+ if [[ -z $ROLE_TO_ASSUME || -z $ACCOUNT_TO_ASSUME ]]; then
echo "$OPTRED ERROR!$OPTNORMAL - Both Account ID (-A) and IAM Role to assume (-R) must be set"
exit 1
fi
diff --git a/prowler b/prowler
index cae80272eb..6246ff3ab1 100755
--- a/prowler
+++ b/prowler
@@ -97,7 +97,7 @@ USAGE:
(i.e.: 123456789012)
-R role name or role arn to assume in the account, requires -A and -T
(i.e.: ProwlerRole)
- -T session duration given to that role credentials in seconds, default 1h (3600) recommended 12h, requires -R and -T
+ -T session duration given to that role credentials in seconds, default 1h (3600) recommended 12h, optional with -R and -A
(i.e.: 43200)
-I External ID to be used when assuming roles (not mandatory), requires -A and -R
-w whitelist file. See whitelist_sample.txt for reference and format
@@ -392,7 +392,7 @@ show_group_title() {
# Function to execute the check
execute_check() {
- if [[ $ACCOUNT_TO_ASSUME ]]; then
+ if [[ -n "${ACCOUNT_TO_ASSUME}" || -n "${ROLE_TO_ASSUME}" ]]; then
# Following logic looks for time remaining in the session and review it
# if it is less than 600 seconds, 10 minutes.
CURRENT_TIMESTAMP=$(date -u "+%s")
@@ -639,7 +639,7 @@ fi
# Gather account data / test aws cli connectivity
getWhoami
-if [[ $ACCOUNT_TO_ASSUME ]]; then
+if [[ -n "${ACCOUNT_TO_ASSUME}" || -n "${ROLE_TO_ASSUME}" ]]; then
assume_role
fi
diff --git a/util/org-multi-account/serverless_codebuild/templates/ProwlerCodeBuildStack.yaml b/util/org-multi-account/serverless_codebuild/templates/ProwlerCodeBuildStack.yaml
index d89c5452e2..bc7c0a2b82 100644
--- a/util/org-multi-account/serverless_codebuild/templates/ProwlerCodeBuildStack.yaml
+++ b/util/org-multi-account/serverless_codebuild/templates/ProwlerCodeBuildStack.yaml
@@ -123,8 +123,12 @@ Resources:
runtime-versions:
python: 3.8
commands:
- - echo "Updating yum..."
+ - echo "Updating yum ..."
- yum -y update
+ - echo "Updating pip ..."
+ - python -m pip install --upgrade pip
+ - echo "Installing requirements ..."
+ - pip install "git+https://github.com/ibm/detect-secrets.git@master#egg=detect-secrets"
build:
commands:
- echo "Running Prowler with script"
diff --git a/util/org-multi-account/serverless_codebuild/templates/ProwlerRole.yaml b/util/org-multi-account/serverless_codebuild/templates/ProwlerRole.yaml
index 138d880976..e5efcd4596 100644
--- a/util/org-multi-account/serverless_codebuild/templates/ProwlerRole.yaml
+++ b/util/org-multi-account/serverless_codebuild/templates/ProwlerRole.yaml
@@ -83,6 +83,7 @@ Resources:
- dax:ListTables
- ds:ListAuthorizedApplications
- ds:DescribeRoles
+ - ec2:GetEbsEncryptionByDefault
- ecr:Describe*
- lambda:GetAccountSettings
- lambda:GetFunctionConfiguration